


┌──(diljot㉿tampere)-[~]
└─$ cat profile.txt
Final-year BEng ICT Bioeconomy student at HAMK, Finland : building a Cyber Threat Intelligence process for a Finnish engineering consultancy as my Bachelor's thesis, applying STIX 2.1/TAXII · MITRE ATT&CK/D3FEND · NIST CSF 2.0 · Diamond Model.
root@kali:~# recon, exploitation, forensics, and OSINT — documented, not just done.
Now shipping Stenwatch: an open-source CTI pipeline that narrows every CVE in the world down to the few that matter to one organisation.


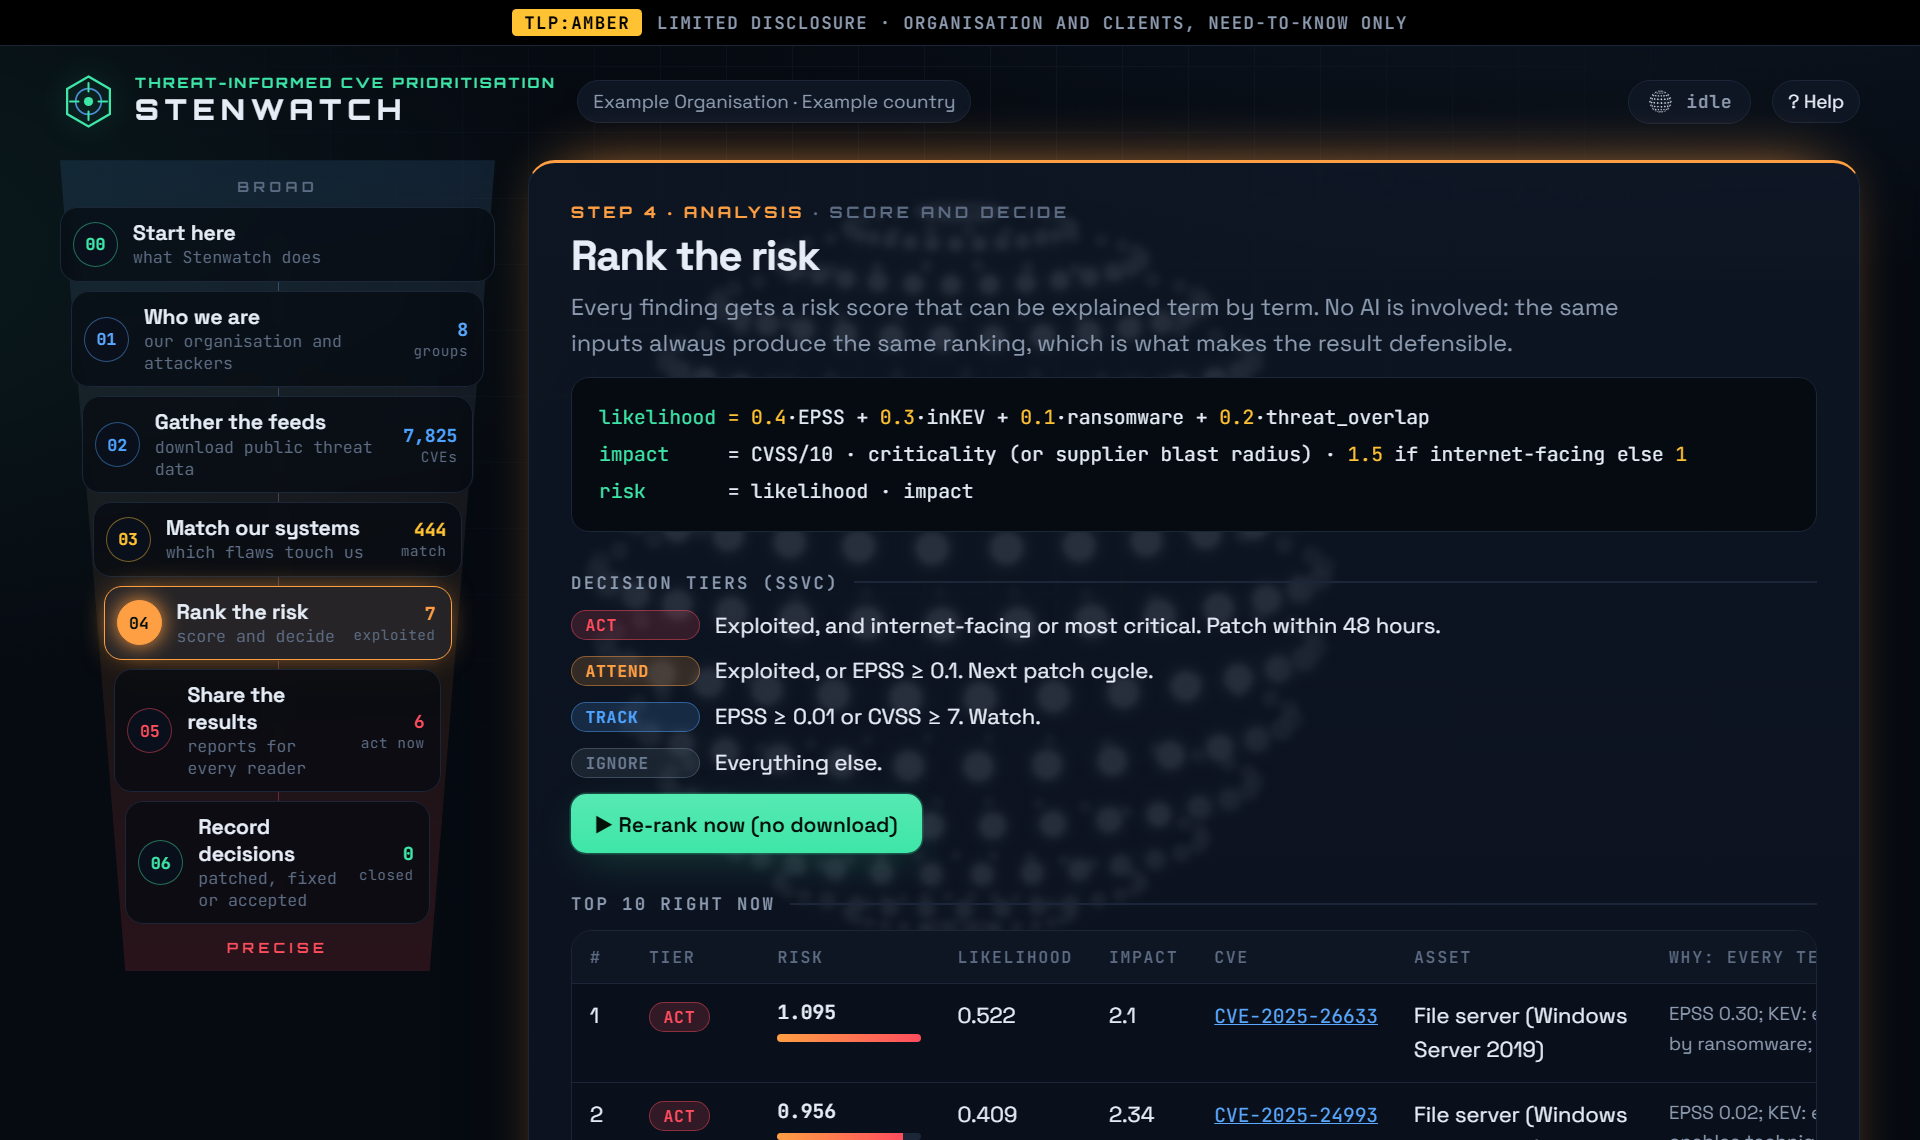
Stenwatch: threat-informed CVE prioritisation. From ~40,000 CVEs a year to the handful attackers are using against you, with a reason for every decision. KEV · EPSS · MITRE ATT&CK · STIX 2.1 · explainable scoring · runs entirely on your machine.


| Repo | What it is |
|---|
| security-portfolio | Consolidated index of all penetration-testing, forensics, and OSINT reports |
| Stenwatch | Threat-informed CVE prioritisation: from every CVE in the world to the few that matter to your organisation. Explainable CTI pipeline with KEV, EPSS, MITRE ATT&CK and STIX 2.1. |
| osint-infrastructure-recon | Infrastructure reconnaissance using Shodan, Censys, DNS/WHOIS enumeration |
| cybersec4europe-forensics | Reconstructed a phishing + SQLi attack chain from Apache logs correlated with Nessus/Nmap/Nikto scans |
| social-engineering-attack-simulation | Simulated social engineering / pretext attack exercise |
| metasploitable2-penetration-test | 10-12 validated exploitable vulns (root bind shell, vsftpd backdoor, Samba/Java RMI RCE) via Nmap + Metasploit, full remediation report |
| iot-data-projects | IoT/embedded sensing projects (Raspberry Pi, data analytics) |
| da-vivian-code-ctf | CTF write-up and solution walkthrough |
| ethical-hacking-lab | General ethical hacking coursework and lab exercises |
| nixu-challenge-ctf | Multi-layer obfuscated flag recovery from a phishing PCAP (Wireshark, CyberChef) + Windows memory forensics (Volatility) |
| osint-self-audit | Self-directed OSINT exposure audit and digital footprint analysis |


root@kali:~# open to junior cybersecurity / IT roles — Finland or remote